Библиотека из npm похищала ключи криптокошельков ещё до запуска приложения
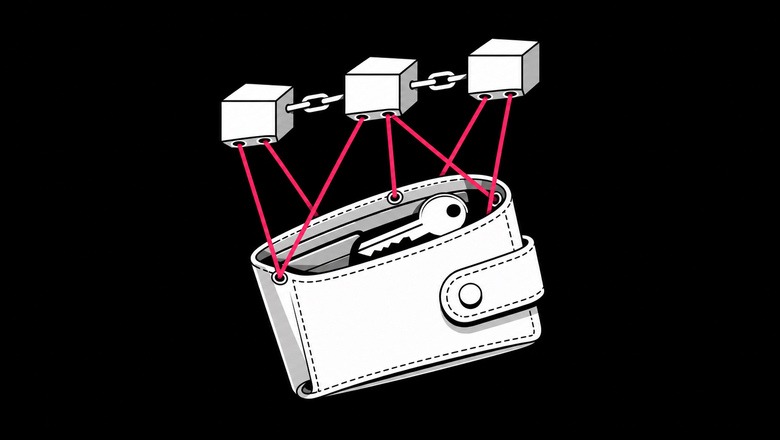
С 9 ноября CodeScoring относит версию 13.3.0 JavaScript-библиотеки @ethersphere/bee-js для распределённого хранилища Swarm к вредоносным. При установке зависимости её код загружал вредонос, который…
Хабр
Full text, translation and AI summary — after signing in
- The full article in your language
- AI summary and translation from the original
- The same account works in the Suviy app
Related coverage
Comments
Sign in to join the conversation. Sign in
No comments yet.